
Описание
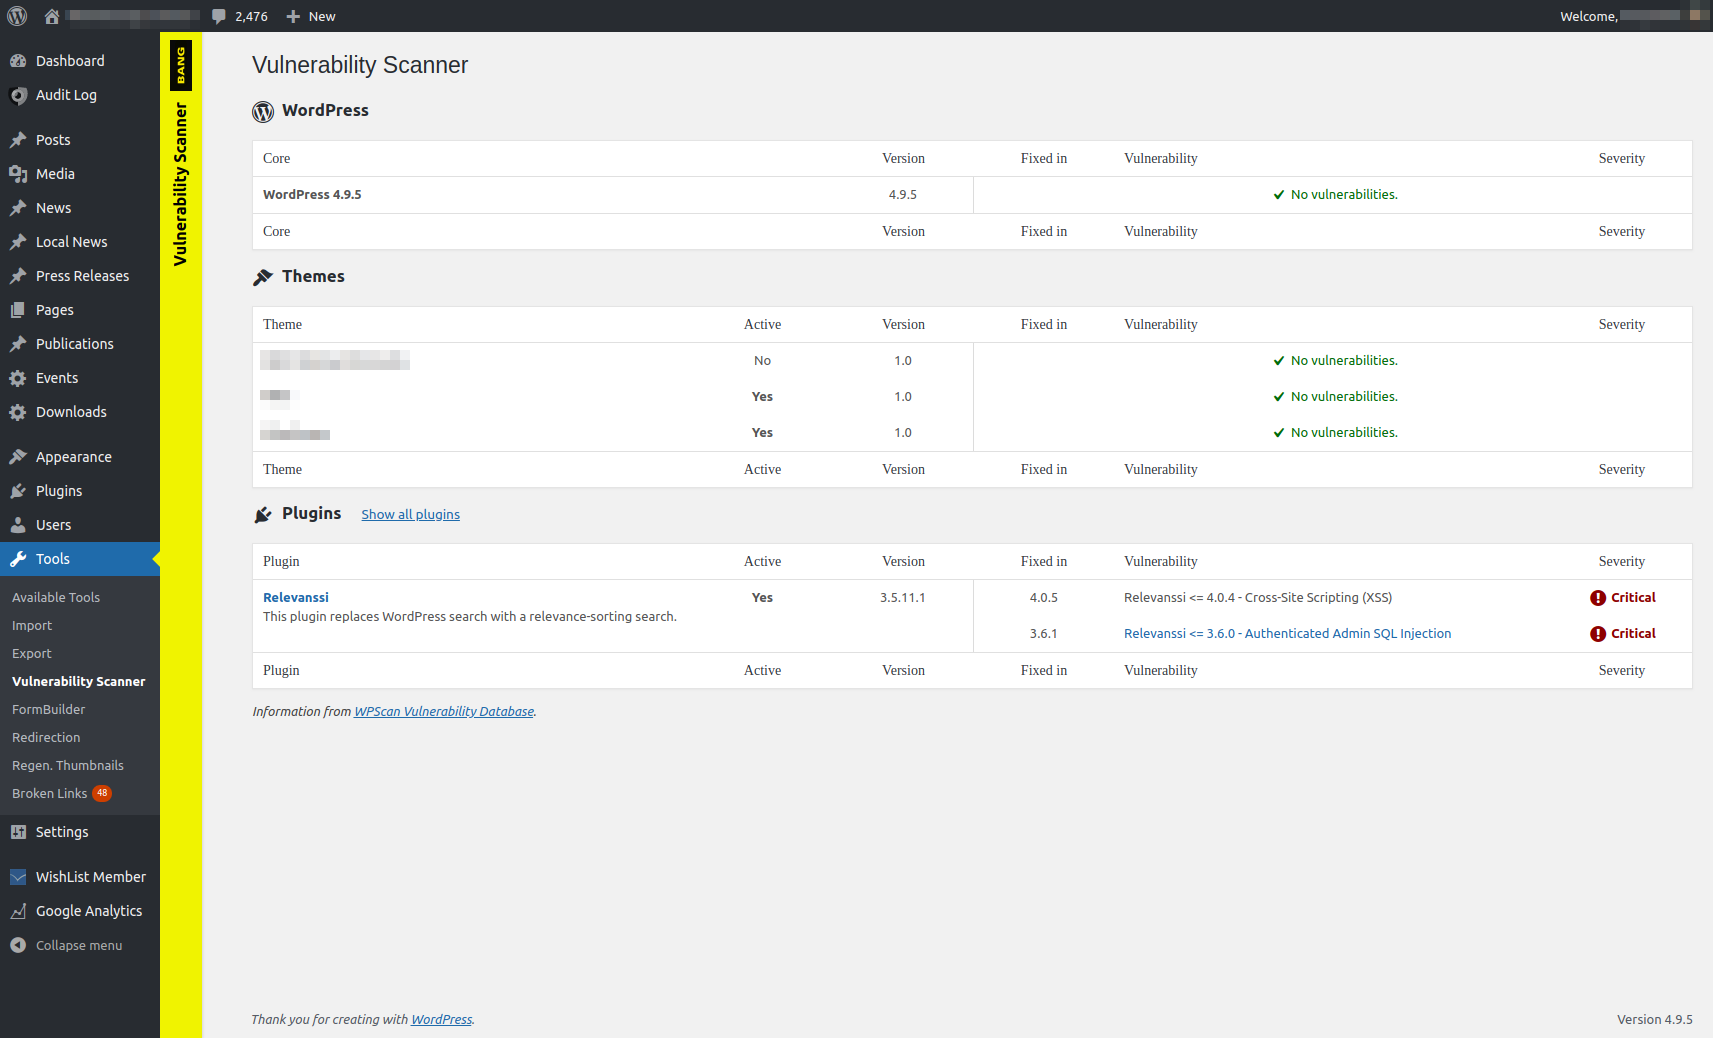
This plugin adds an admin page under the Tools section that reports on any known vulnerabilities in your version of WordPress and any installed themes or plugins.
This information is only visible to administrators (or more precisely, those with the manage_options capability). Subscribers, authors and editors cannot see the data.
Source
The information this plugin uses comes from the WPScan Vulnerability Database: https://wpvulndb.com/. It uses a cache and internal throttling to ensure its use of the API is not excessive or abusive.
Note
Using this plugin does not guarantee that your site has no vulnerabilities. It also does not absolve you from responsibilities as a site owner to secure your site in other ways, such as SSL or host security. This plugin is only a tool; using it responsibly is up to you.
WP-CLI
This plugin registers a WP-CLI command, that allows you to scan from the command line. The response codes are compatible with Nagios (1 for critical error, 2 for warning, 3 for unknown).
wp vuln scan, to report all known vulnerabilities.wp vuln plugins, to report only vulnerabilities in plugins.wp vuln themes, to report only vulnerabilities in themes.wp vuln wp, to report only vulnerabilities in WordPress core.wp vuln details, to show a more detailed output on known vulnerabilities.wp vuln clear, to clear the internal cache of vulnerability data. This will result in making extra requests to the API, and is probably not needed.
Снимки на разширението
Инсталиране
- Upload the whole
bang-vulnerability-scannerdirectory to the/wp-content/plugins/directory - Activate the plugin through the ‘Plugins’ menu in WordPress
- Find the vulnerability scanner in the ‘Tools’ menu in WordPress
ЧЗВ
- Installation Instructions
-
- Upload the whole
bang-vulnerability-scannerdirectory to the/wp-content/plugins/directory - Activate the plugin through the ‘Plugins’ menu in WordPress
- Find the vulnerability scanner in the ‘Tools’ menu in WordPress
- Upload the whole
Отзиви
There are no reviews for this plugin.
Сътрудници и разработчици
“Bang Vulnerability Scanner” е софтуер с отворен код. Към разширението са допринесли следните хора:
Сътрудници
Превеждане на “Bang Vulnerability Scanner” на вашия език.
Имате интерес към разработване?
Преглеждане на кода, разглеждане на SVN хранилище, или абонамент към програмната история (log) чрез RSS.
Списък с промени
1.0
- Initial release